AutoFlow
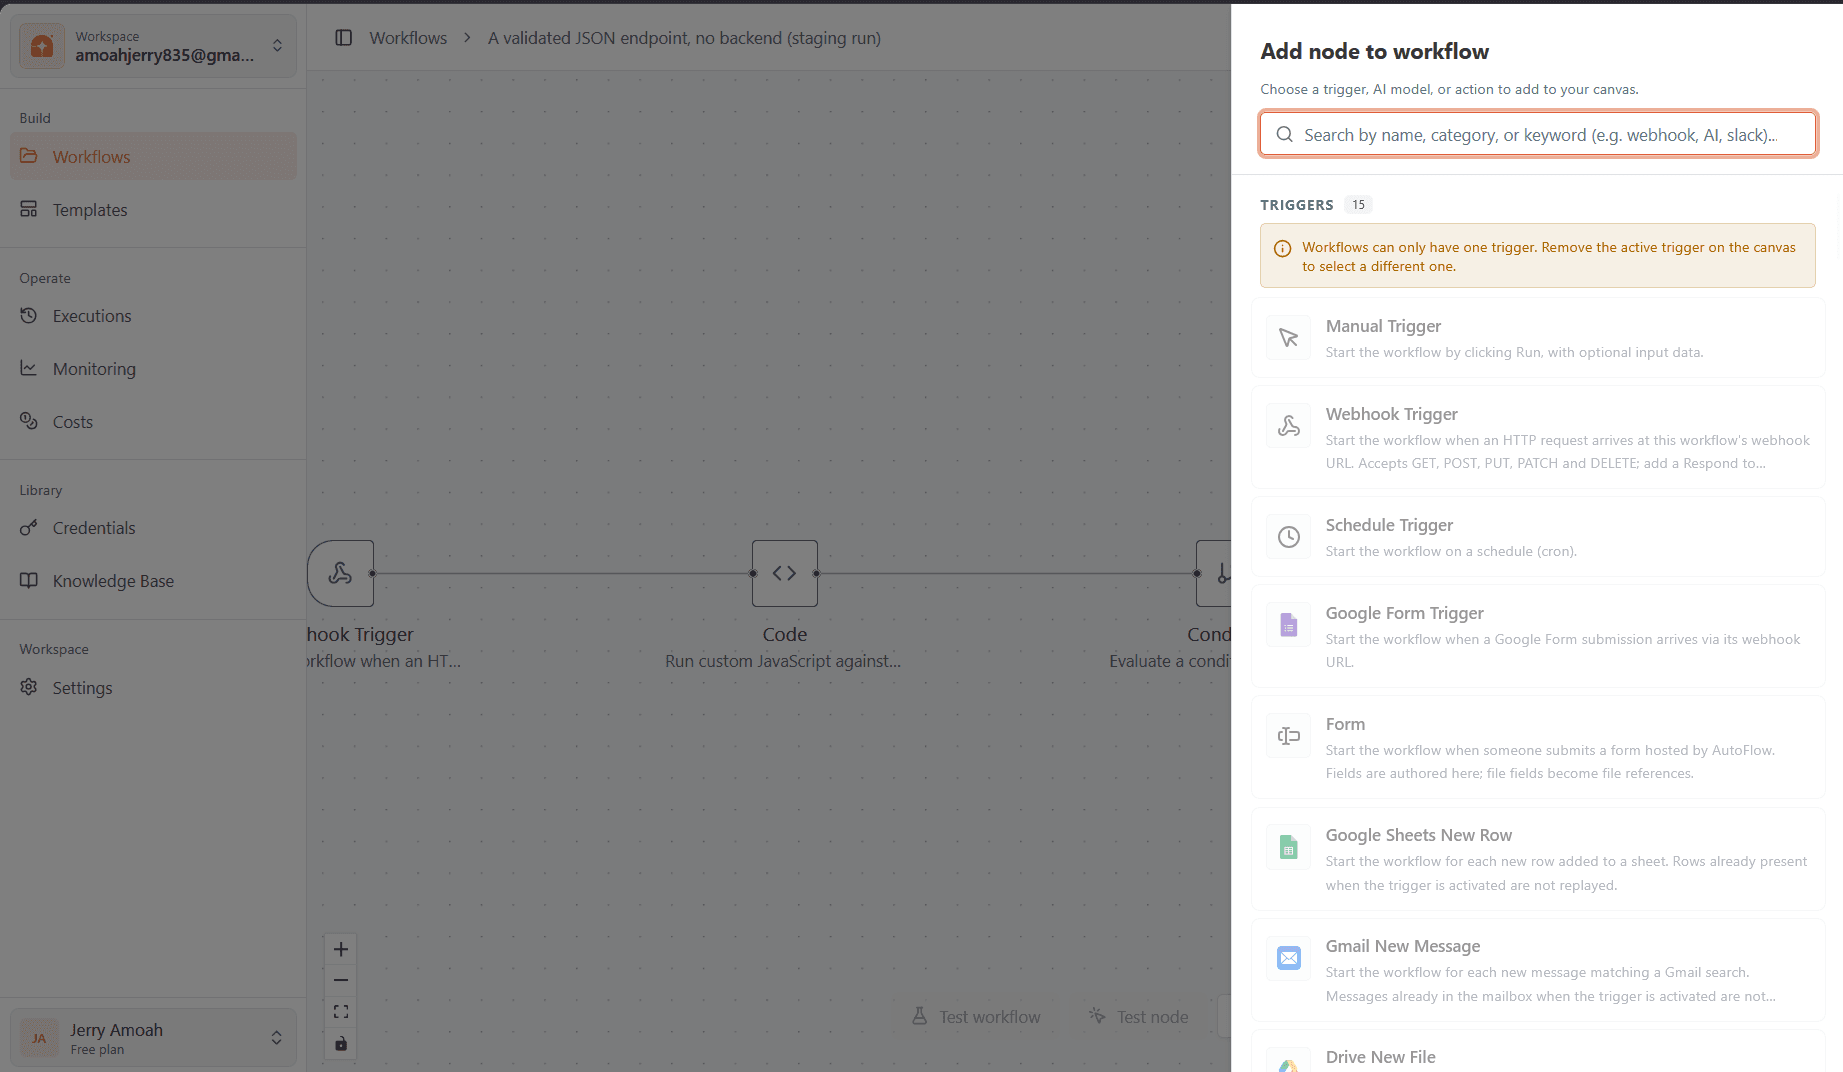
An open-source automation platform: build workflows as node graphs on a visual canvas and run them on a durable execution engine — triggers, HTTP calls, AI models and chat deliveries, chained together.
Origin — Started from a Code With Antonio course project and extended well beyond it: multi-tenant RBAC and audit logging, the encrypted credential vault, the AI provider registry, the pgvector knowledge base and 25 decision records.
The problem
Automation tools make you choose: no-code builders that stall on anything real, or self-hosted engines that come with a DevOps job attached. AutoFlow aims for the power of n8n without that burden — so durable execution, multi-tenant security and AI cost control have to be built in, not bolted on.
n8n's power without the DevOps burden.
Results
From the project's progress log, Sep 2026The build
A Next.js 15 app with a tRPC API and a React Flow canvas. Workflows compile to a plan that runs on Inngest: every node executes inside a durable step, so a crashed run resumes without repeating side effects. Credentials live in an envelope-encrypted vault, and every read and write is scoped to the organisation.
Inngest as the durable runtime
Each node runs inside step.run, so completed nodes are memoised and a resumed run never repeats a side effect. Cron, concurrency keys and cancellation come with it — no queue, workers or scheduler to operate.
Expressions are parsed, not evaluated
Template expressions are parsed into a path and resolved against the run context. No eval, no new Function, no vm on the request or execution path — remote code execution is closed by construction, not by a sandbox.
No plaintext read path for credentials
Each credential gets its own AES-256-GCM data key, wrapped by a master key that never touches the database. No endpoint returns decrypted material — not to the owner, not to an admin, not for a test button.
What I'd do differently
Docs drift from code. In August an audit found the progress log claiming things the code didn't do — and missing things it did. I rewrote it so every claim points at a file, and it's now updated in the same pull request as the change.
Writing decision records before code. Twenty-five ADRs in, the hardest calls — sandboxing, SSRF, credential handling — are each explained in one place.